


Cisco 300-710 Daily Practice Exam New 2022 Updated 225 Questions
Use Valid 300-710 Exam - Actual Exam Question & Answer
Skills Measured by 300-710
To get the passing score in the official test, the candidates must address the following skills as described below:
- Management & Troubleshooting — here, candidates must show they have the ability to adjust dashboards & analytics in Firepower Management Center, troubleshoot problems with the help of GUI & FMC CLI, anticipate risks, create reports, and lastly, use packet capture methods to carry out troubleshooting.
- Integration — in the final domain, students must demonstrate their ability to deploy Threat Intelligence Director when investigating security intelligence feeds from third parties, use Firepower Management Center to tweak Cisco AMP for endpoints and networks, explain the Cisco Identify Services Engine (ISE) & the Cisco FMC PxGrid Integration, carry out security checks with the help of the Cisco Threat Response, and finally, detail the use of the Rapid Threat Containment (RTC) feature found inside FMC.
- Configuration — under this exam category, examinees will have to tweak the system configurations of Cisco Firepower Management Center and set up policies such as SSL, intrusion, malware & file, access control, identity, DNS, and pre-filter necessary for the Cisco Firepower Management Center. What is more, applicants will have to be aware of how to use that Center to adjust numerous aspects such as correlation, network discovery, actions, application detectors & Open AppID, intrusion rules & objects, and tweak various devices including QoS, NAT, Platform Settings, VPN, Certificates, and Device Management.
- Deployment — for the initial part, students must be able to incorporate NGFW modes such as transparent & routed ones, deploy NGIPS such as Inline & Passive, incorporate high availability facilities like standby/active failover, link redundancy, and multi-instance, and finally, explain IRB settings.
Who should take the Securing Networks with Cisco Firepower (300-710 SNCF) Exam
People who wish to explore the power of the dynamic culture of the Cisco Learning Network to jump-start their certification and lifelong learning goals should take this exam. Those who want to get useful tools for IT training for all Cisco certifications should also get this certification. People with prior knowledge of Cisco Firepower Threat Defence, including policy configurations, integrations, deployments, management and troubleshooting, are highly recommended to take this exam and get themselves certified from Cisco.
List of target audience for this exam:
- System engineers
- Security consultants
- Cisco integrators and partners
- Security administrators
- Technical support personnel
NEW QUESTION 114
A network administrator reviews the file report for the last month and notices that all file types, except exe. show a disposition of unknown. What is the cause of this issue?
- A. Only Spero file analysis is enabled.
- B. The malware license has not been applied to the Cisco FTD.
- C. A file policy has not been applied to the access policy.
- D. The Cisco FMC cannot reach the Internet to analyze files.
Answer: B
NEW QUESTION 115
Which CLI command is used to control special handling of ClientHello messages?
- A. system support ssl-client-hello-tuning
- B. system support ssl-client-hello-display
- C. system support ssl-client-hello-enabled
- D. system support ssl-client-hello-force-reset
Answer: C
Explanation:
Explanation
Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/610/configuration/guide/fpmc-config-guide-v61/firepower_command_line_reference.html
NEW QUESTION 116
An administrator must use Cisco FMC to install a backup route within the Cisco FTD to route traffic in case of a routing failure with the primary route. Which action accomplishes this task?
- A. Configure EIGRP routing on the FMC to ensure that dynamic routes are always updated.
- B. Create the backup route and use route tracking on both routes to a destination IP address in the network.
- C. Install the static backup route and modify the metric to be less than the primary route.
- D. Use a default route on the FMC instead of having multiple routes contending for priority.
Answer: C
NEW QUESTION 117
Which protocol establishes network redundancy in a switched Firepower device deployment?
- A. GLBP
- B. HSRP
- C. VRRP
- D. STP
Answer: D
Explanation:
Section: Deployment
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config- guide-v62/firepower_threat_defense_high_availability.html
NEW QUESTION 118
With Cisco FTD software, which interface mode must be configured to passively receive traffic that passes through the appliance?
- A. IPS-only
- B. tap
- C. ERSPAN
- D. firewall
Answer: C
NEW QUESTION 119
Which connector is used to integrate Cisco ISE with Cisco FMC for Rapid Threat Containment?
- A. FMC RTC
- B. ISEGrid
- C. pxGrid
- D. FTD RTC
Answer: C
NEW QUESTION 120
Which report template field format is available in Cisco FMC?
- A. benchmark chart
- B. arrow chart
- C. box lever chart
- D. bar chart
Answer: D
NEW QUESTION 121
Which command is typed at the CLI on the primary Cisco FTD unit to temporarily stop running high- availability?
- A. system support network-options
- B. configure high-availability disable
- C. configure high-availability resume
- D. configure high-availability suspend
Answer: B
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/610/configuration/guide/fpmc-config- guide-v61/firepower_threat_defense_high_availability.html
NEW QUESTION 122
An engineer configures an access control rule that deploys file policy configurations to security zone or tunnel zones, and it causes the device to restart. What is the reason for the restart?
- A. Source or destination security zones in the source tunnel zone do not match the security zones that are associated with interfaces on the target devices.
- B. The source tunnel zone in the rule does not match a tunnel zone that is assigned to a tunnel rule in the source policy.
- C. The source tunnel zone in the rule does not match a tunnel zone that is assigned to a tunnel rule in the destination policy.
- D. Source or destination security zones in the access control rule matches the security zones that are associated with interfaces on the target devices.
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/623/configuration/guide/fpmc-config-guide-v623/policy_management.html
NEW QUESTION 123
After deploying a network-monitoring tool to manage and monitor networking devices in your organization, you realize that you need to manually upload an MIB for the Cisco FMC. In which folder should you upload the MIB file?
- A. /sf/etc/DCEALERT.MIB
- B. /etc/sf/DCEALERT.MIB
- C. system/etc/DCEALERT.MIB
- D. /etc/sf/DCMIB.ALERT
Answer: B
Explanation:
Section: Management and Troubleshooting
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/firesight/541/firepower-module-user-guide/asa- firepower-module-user-guide-v541/Intrusion-External-Responses.pdf
NEW QUESTION 124
When do you need the file-size command option during troubleshooting with packet capture?
- A. when capture packets are restricted from the secondary memory
- B. when capture packets are less than 16 MB
- C. when capture packets exceed 32 MB
- D. when capture packets exceed 10 GB
Answer: C
NEW QUESTION 125
What is the result of specifying of QoS rule that has a rate limit that is greater than the maximum throughput of an interface?
- A. The rate-limiting rule is disabled.
- B. The system repeatedly generates warnings.
- C. Matching traffic is not rate limited.
- D. The system rate-limits all traffic.
Answer: C
Explanation:
Section: Configuration
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config- guide-v62/quality_of_service_qos.pdf
NEW QUESTION 126
A company is in the process of deploying intrusion prevention with Cisco FTDs managed by a Cisco FMC. An engineer must configure policies to detect potential intrusions but not block the suspicious traffic. Which action accomplishes this task?
- A. Configure IPS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by checking the "Drop when inline" option.
- B. Configure IPS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by unchecking the "Drop when inline" option.
- C. Configure IDS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by unchecking the "Drop when inline" option.
- D. Configure IDS mode when creating or editing a policy rule under the Cisco FMC Intrusion tab in Access Policies section by checking the "Drop when inline" option.
Answer: C
NEW QUESTION 127
Which command should be used on the Cisco FTD CLI to capture all the packets that hit an interface?
- A. capture
- B. capture WORD
- C. configure coredump packet-engine enable
- D. capture-traffic
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/command_ref/ b_Command_Reference_for_Firepower_Threat_Defense/ac_1.html
NEW QUESTION 128
With Cisco Firepower Threat Defense software, which interface mode must be configured to passively receive traffic that passes through the appliance?
- A. inline set
- B. inline tap
- C. routed
- D. passive
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/640/configuration/guide/fpmc-config- guide-v64/interface_overview_for_firepower_threat_defense.html
NEW QUESTION 129
Refer to the exhibit.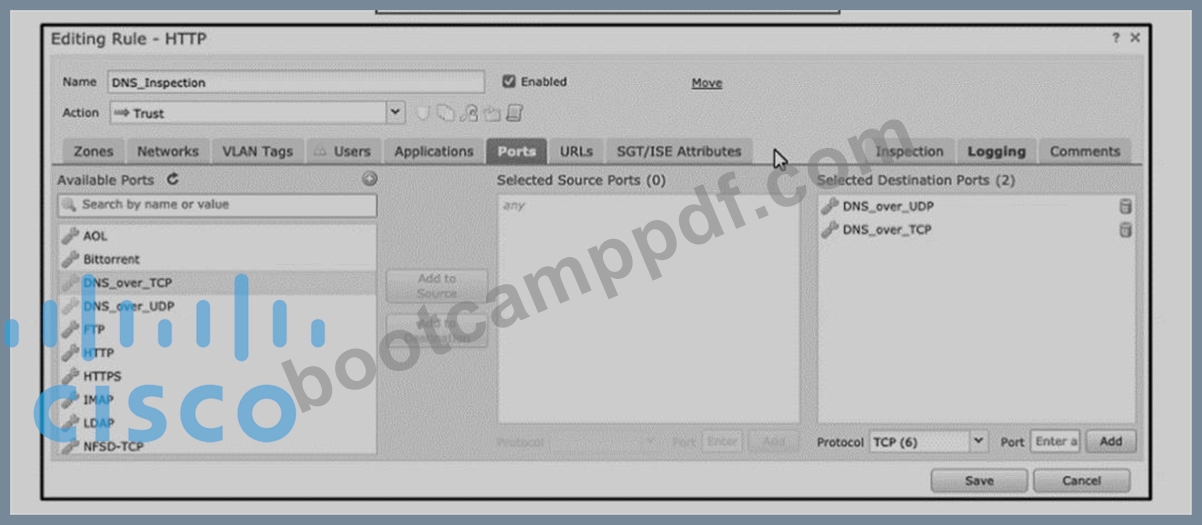
Refer to the exhibit An engineer is modifying an access control pokey to add a rule to inspect all DNS traffic that passes through the firewall After making the change and deploying the pokey they see that DNS traffic is not bang inspected by the Snort engine What is the problem?
- A. The rule is configured with the wrong setting for the source port
- B. The rule must specify the security zone that originates the traffic
- C. The action of the rule is set to trust instead of allow.
- D. The rule must define the source network for inspection as well as the port
Answer: C
NEW QUESTION 130
Which Cisco Firepower feature is used to reduce the number of events received in a period of time?
- A. rate-limiting
- B. suspending
- C. correlation
- D. thresholding
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firesight/541/firepower-module-user-guide/asa- firepower-module-user-guide-v541/Intrusion-Global-Threshold.html
NEW QUESTION 131
A Cisco FTD device is running in transparent firewall mode with a VTEP bridge group member ingress interface What must be considered by an engineer tasked with specifying a destination MAC address for a packet trace?
- A. Only the UDP packet type is supported
- B. The destination MAC address is optional if a VLAN ID value is entered
- C. The VLAN ID and destination MAC address are optional
- D. The output format option for the packet logs unavailable
Answer: B
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/firepower/620/configuration/guide/fpmc-config-guide-v62/troubleshooting_the_system.html
NEW QUESTION 132
What is the maximum bit size that Cisco FMC supports for HTTPS certificates?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: C
Explanation:
Reference: https://www.cisco.com/c/en/us/td/docs/security/firepower/610/configuration/guide/fpmc-config- guide-v61/system_configuration.html
NEW QUESTION 133
Which command must be run to generate troubleshooting files on an FTD?
- A. system support view-files
- B. show tech-support
- C. sudo sf_troubleshoot.pl
- D. system generate-troubleshoot all
Answer: D
Explanation:
Reference: https://www.cisco.com/c/en/us/support/docs/security/sourcefire-defense-center/117663-technote- SourceFire-00.html
NEW QUESTION 134
......
Test Engine to Practice 300-710 Test Questions: https://www.bootcamppdf.com/300-710_exam-dumps.html
300-710 Real Exam Questions Test Engine Dumps Training With 225 Questions: https://drive.google.com/open?id=1qDJSFjk50yareYWFgoNre_3qOfWXmtBm