


Best Quality Microsoft SC-200 Exam Questions BootcampPDF Realistic Practice Exams [2021]
Critical Information To Microsoft Security Operations Analyst Pass the First Time
NEW QUESTION 51
You use Azure Defender.
You have an Azure Storage account that contains sensitive information.
You need to run a PowerShell script if someone accesses the storage account from a suspicious IP address.
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Create an Azure logic app that has an Azure Security Center alert trigger.
- B. From Azure Security Center, enable workflow automation.
- C. Create an Azure logic appthat has an HTTP trigger.
- D. From Azure Active Directory (Azure AD), add an app registration.
- E. Create an Azure logic appthat has a manual trigger
Answer: A,B
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/storage/common/azure-defender-storage-configure?tabs=azure-security-center
https://docs.microsoft.com/en-us/azure/security-center/workflow-automation
NEW QUESTION 52
You plan to connect an external solution that will send Common Event Format (CEF) messages to Azure Sentinel.
You need to deploy the log forwarder.
Which three actions should you perform in sequence? To answer, move the appropriate actions form the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation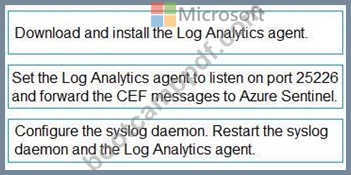
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/connect-cef-agent?tabs=rsyslog
NEW QUESTION 53
You are informed of a new common vulnerabilities and exposures (CVE) vulnerability that affects your environment.
You need to use Microsoft Defender Security Center to request remediation from the team responsible for the affected systems if there is a documented active exploit available.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
Reference:
https://techcommunity.microsoft.com/t5/core-infrastructure-and-security/microsoft-defender-atp-remediate-apps
NEW QUESTION 54
You open the Cloud App Security portal as shown in the following exhibit.
You need to remediate the risk for the Launchpad app.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - Select the app.
2 - Tag the app as Unsanctioned.
3 - Generate a block script.
4 - Run the script on the source appliance.
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/governance-discovery
NEW QUESTION 55
DRAG DROP
You open the Cloud App Security portal as shown in the following exhibit.
Your environment does NOT have Microsoft Defender for Endpoint enabled.
You need to remediate the risk for the Launchpad app.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Select and Place:
Answer:
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/cloud-app-security/governance-discovery
NEW QUESTION 56
You create a custom analytics rule to detect threats in Azure Sentinel.
You discover that the rule fails intermittently.
What are two possible causes of the failures? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. The target workspace was deleted.
- B. Permissions to the data sources of the rule query were modified.
- C. The rule query takes too long to run and times out.
- D. There are connectivity issues between the data sources and Log Analytics
Answer: C,D
Explanation:
Section: [none]
Explanation:
Incorrect Answers:
B: This would cause it to fail every time, not just intermittently.
C: This would cause it to fail every time, not just intermittently.
NEW QUESTION 57
HOTSPOT
You have a Microsoft 365 E5 subscription.
You plan to perform cross-domain investigations by using Microsoft 365 Defender.
You need to create an advanced hunting query to identify devices affected by a malicious email attachment.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Answer:
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/mtp/advanced-hunting-query-emails-devices?
view=o365-worldwide
NEW QUESTION 58
You use Azure Sentinel to monitor irregular Azure activity.
You create custom analytics rules to detect threats as shown in the following exhibit.
You do NOT define any incident settings as part of the rule definition.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-detect-threats-custom
NEW QUESTION 59
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Microsoft Defender for Identity integration with Active Directory.
From the Microsoft Defender for identity portal, you need to configure several accounts for attackers to exploit.
Solution: From Entity tags, you add the accounts as Honeytoken accounts.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/defender-for-identity/manage-sensitive-honeytoken-accounts
NEW QUESTION 60
From Azure Sentinel, you open the Investigation pane for a high-severity incident as shown in the following exhibit.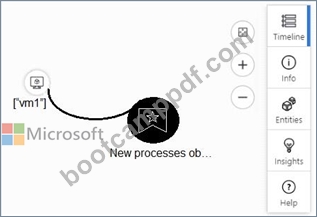
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/tutorial-investigate-cases#use-the-investigation-graph-to-deep-dive
NEW QUESTION 61
You need to implement Azure Defender to meet the Azure Defender requirements and the business requirements.
What should you include in the solution? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: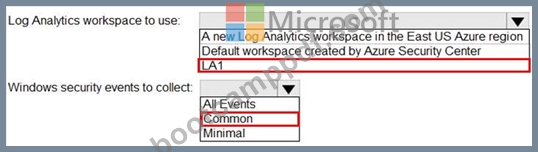
NEW QUESTION 62
You are investigating a potential attack that deploys a new ransomware strain.
You plan to perform automated actions on a group of highly valuable machines that contain sensitive information.
You have three custom device groups.
You need to be able to temporarily group the machines to perform actions on the devices. Which three actions should you perform? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A. Create a new admin role.
- B. Create a new device group that has a rank of 4.
- C. Add a tag to the device group.
- D. Create a new device group that has a rank of 1.
- E. Add the device users to the admin role.
- F. Add a tag to the machines.
Answer: C,D,F
NEW QUESTION 63
You plan to create a custom Azure Sentinel query that will track anomalous Azure Active Directory (Azure AD) sign-in activity and present the activity as a time chart aggregated by day.
You need to create a query that will be used to display the time chart. What should you include in the query?
- A. bin
- B. extend
- C. workspace
- D. makeset
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/azure-monitor/logs/get-started-queries
NEW QUESTION 64
You are investigating an incident in Azure Sentinel that contains more than 127 alerts.
You discover eight alerts in the incident that require further investigation.
You need to escalate the alerts to another Azure Sentinel administrator.
What should you do to provide the alerts to the administrator?
- A. Create a scheduled query rule
- B. Share the incident URL
- C. Assign the incident
- D. Create a Microsoft incident creation rule
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/investigate-cases
NEW QUESTION 65
You have an Azure Functions app that generates thousands of alerts in Azure Security Center each day for normal activity.
You need to hide the alerts automatically in Security Center.
Which three actions should you perform in sequence in Security Center? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
1 - Select Security policy.
2 - Select Suppression rules, and then select Create new suppression rule.
3 - Select Azure Resource as the entity type and specify the ID.
Reference:
https://techcommunity.microsoft.com/t5/azure-security-center/suppression-rules-for-azure-security-center-alerts-are-now/ba-p/1404920
NEW QUESTION 66
You are configuring Azure Sentinel.
You need to send a Microsoft Teams message to a channel whenever an incident representing a sign-in risk event is activated in Azure Sentinel.
Which two actions should you perform in Azure Sentinel? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. Associate a playbook to the analytics rule that triggered the incident.
- B. Enable Entity behavior analytics.
- C. Add a playbook.
- D. Enable the Fusion rule.
- E. Create a workbook.
Answer: A,B
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/sentinel/enable-entity-behavior-analytics
https://docs.microsoft.com/en-us/azure/sentinel/automate-responses-with-playbooks
NEW QUESTION 67
You need to receive a security alert when a user attempts to sign in from a location that was never used by the other users in your organization to sign in.
Which anomaly detection policy should you use?
- A. Activity from infrequent country
- B. Malware detection
- C. Activity from anonymous IP addresses
- D. Impossible travel
Answer: A
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/cloud-app-security/anomaly-detection-policy
NEW QUESTION 68
You need to implement the Azure Information Protection requirements.
What should you configure first?
- A. Advanced features from Settings in Microsoft Defender Security Center
- B. Device health and compliance reports settings in Microsoft Defender Security Center
- C. content scan jobs in Azure Information Protection from the Azure portal
- D. scanner clusters in Azure Information Protection from the Azure portal
Answer: A
Explanation:
Explanation/Reference:
https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft-defender-atp/information- protection-in-windows-overview
NEW QUESTION 69
......
Exam SC-200: Microsoft Security Operations Analyst
The Microsoft Security Operations Analyst collaborates with organizational stakeholders to secure information technology systems for the organization. Their goal is to reduce organizational risk by rapidly remediating active attacks in the environment, advising on improvements to threat protection practices, and referring violations of organizational policies to appropriate stakeholders.
Responsibilities include threat management, monitoring, and response by using a variety of security solutions across their environment. The role primarily investigates, responds to, and hunts for threats using Microsoft Azure Sentinel, Azure Defender, Microsoft 365 Defender, and third-party security products. Since the Security Operations Analyst consumes the operational output of these tools, they are also a critical stakeholder in the configuration and deployment of these technologies.
Part of the requirements for: Microsoft Certified: Security Operations Analyst Associate
Schedule exam
Languages: English, Japanese, Chinese (Simplified), Korean, French, German, Spanish, Portuguese (Brazil), Russian, Arabic (Saudi Arabia), Chinese (Traditional), Italian
Retirement date: none
This exam measures your ability to accomplish the following technical tasks: mitigate threats using Microsoft 365 Defender; mitigate threats using Azure Defender; and mitigate threats using Azure Sentinel.
SC-200 EXAM DUMPS WITH GUARANTEED SUCCESS: https://www.bootcamppdf.com/SC-200_exam-dumps.html
Best Quality Microsoft SC-200 Exam Questions: https://drive.google.com/open?id=173tq8bGFRX0KMnud-rXKKw3Ygwmnjvvz